

Cybersecurity For Developers: From Basics To Best Practices
Published 9/2024
MP4 | Video: h264, 1920×1080 | Audio: AAC, 44.1 KHz
Learn essential cybersecurity practices for developers through real-world web application examples & develop secure APIs
What you’ll learn
Learn best practices for securing APIs against common threats
Insights into secure coding practices
Identify key tools and techniques for API security assessment
Gain hands-on experience with real-world API security scenarios
Explore mitigation strategies for each OWASP vulnerability
Knowledge of security tools and frameworks used in the industry
Develop a robust API security strategy for your applications
Understand the importance of authentication and authorization in APIs
Learn how to perform effective security testing on APIs
Understand the OWASP API Top 10 vulnerabilities and their impact on security
Learn how to secure sensitive data in API responses
Explore the risks of improper CORS configurations in APIs
Gain skills in implementing OAuth and JWT for API security
Discover how to handle API versioning securely
Learn about the security aspects of API design and architecture
Understand the role of security audits and reviews in API development
Get practical tips for threat modeling specific to APIs
Explore strategies for incident response in API security breaches
Strategies for continuous security monitoring and improvement
Requirements
Basic understanding of web development concepts
Familiarity with RESTful APIs and HTTP protocols
Knowledge of security principles is a plus but not mandatory
No specific tools are required; just a computer with internet access
A willingness to learn and explore API security topics
Description
Overview
Section 1: Introduction
Lecture 1 Communication plan
Lecture 2 Introduction to Cybersecurity and the Role of OWASP
Section 2: OWASP Top 10 2021
Lecture 3 OWASP Top 10: Overview
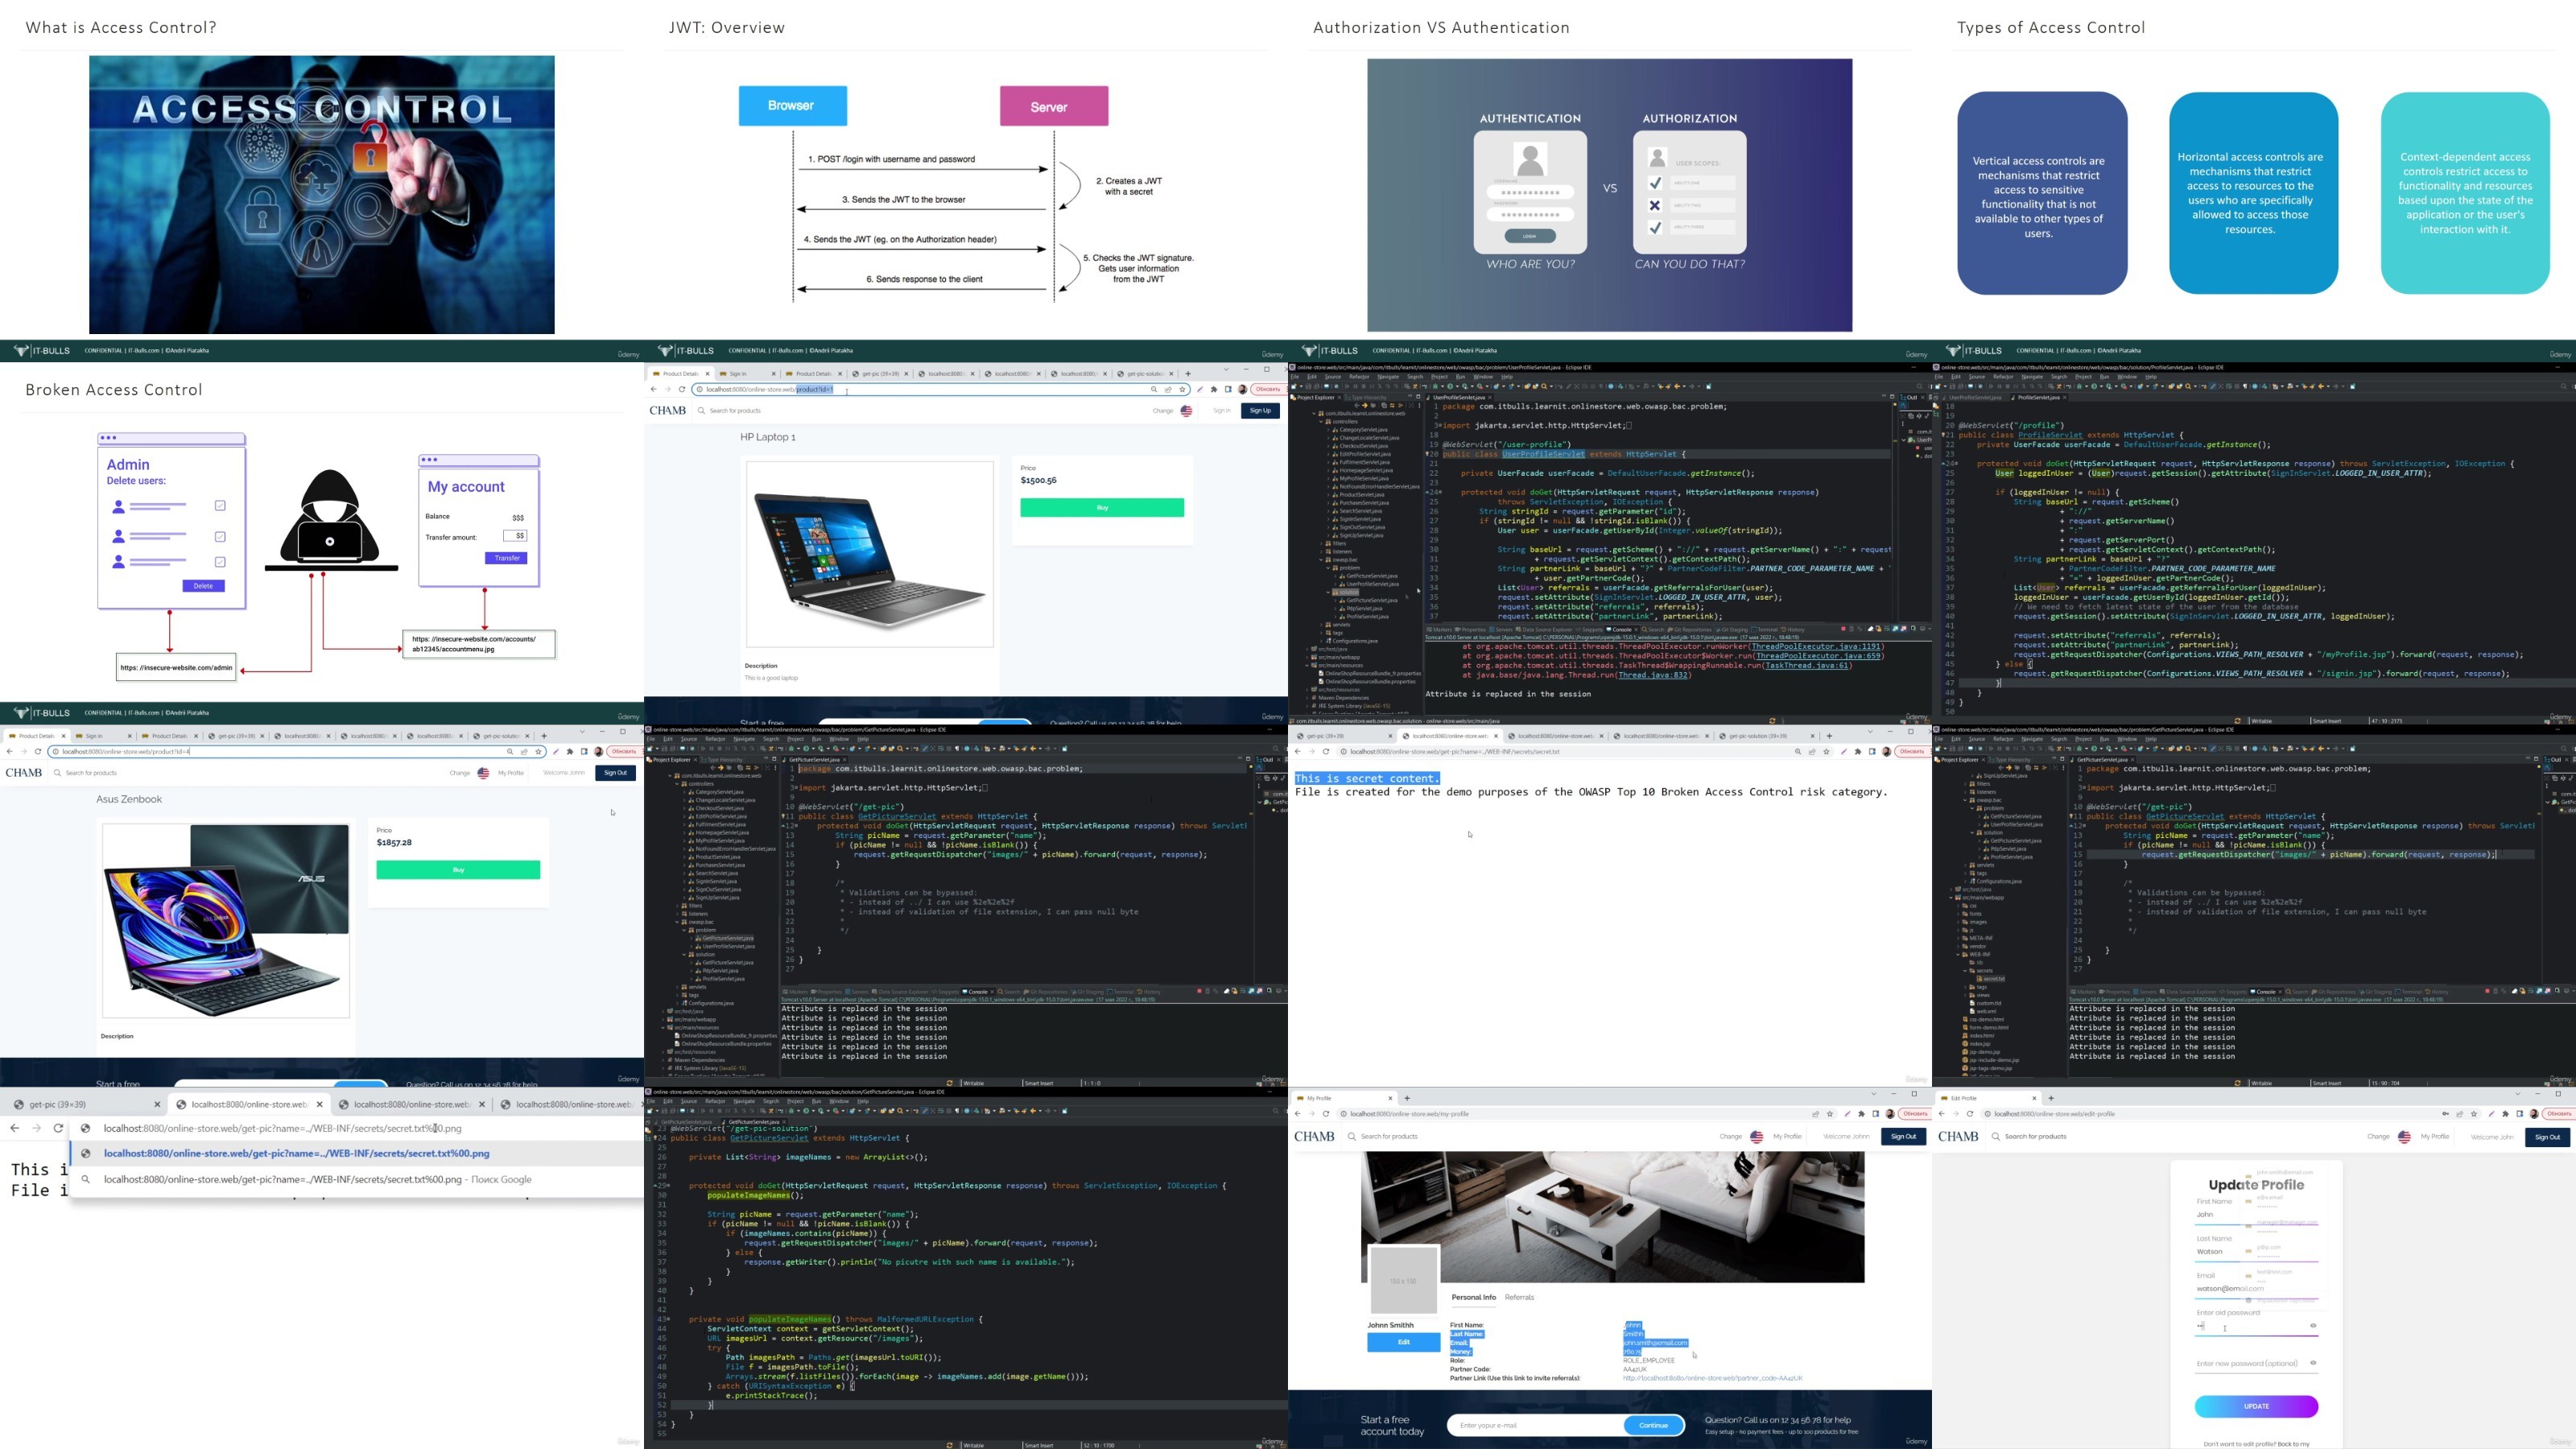
Lecture 4 Broken Access Control
Lecture 5 Cryptography Failures (Theory, Sensitive Data, Data Breach, Types of Failures)
Lecture 6 Cryptography Failures (Practical Examples, SQL Injections, TLS/SSL, HTTPS)
Lecture 7 Cryptography Failures (Examples, Password Encryption, Hashing, Salting)
Lecture 8 Injection (Overview, Fuzzing, CWEs, Impact, Injection Types, Command Injection)
Lecture 9 Injection (Cross Site Scripting, Types of XSS, SQL, JPA, NoSQL Injections)
Lecture 10 Injection (XPath Injection, Log Injection, Input Validation)
Lecture 11 Insecure Design (Overivew, CWEs, Shift Left Security, Threat Modeling Manifesto)
Lecture 12 Insecure Design (Secure Design Process, Security Controls, Metrics, Examples)
Lecture 13 Security Misconfiguration (Overview, CWEs, Types, Real-life attacks)
Lecture 14 Security Misconfiguration (Hardening, Zero Trust, Defense in Depth, Practice)
Lecture 15 Vulnerable & Outdated Components
Lecture 16 Identification & Authentication Failures
Lecture 17 Software & Data Integrity Failures
Lecture 18 Security Logging & Monitoring Failures
Lecture 19 Server-Side Request Forgery (SSRF)
Section 3: OWASP API Top 10 2023
Lecture 20 OWASP API Security Project & OWASP API Security Top 10 2023
Lecture 26 API2:2023 Broken Authentication – P.3 – (Practice, JWT Tokens, Timing Attacks)
Lecture 36 API7:2023 – Server Side Request Forgery
Lecture 37 API8:2023 – Security Misconfiguration
Section 4: Bonus section
Lecture 42 Bonus lesson
Developers looking to enhance their API security skills,Security professionals seeking to understand the latest API vulnerabilities,Software engineers interested in building secure applications,Students and beginners eager to learn about API security best practices,Tech leads and architects wanting to implement robust security measures in their projects,IT Managers and Team Leads: Professionals responsible for overseeing security measures in their organizations and ensuring best practices are followed.
RapidGator
https://www.keeplinks.org/p27/68b393e660540
NitroFlare
https://www.keeplinks.org/p27/68b3963905ba3
DDownload
https://www.keeplinks.org/p27/68b397f06d335