


Isc2 Cissp Full Course & Practice Exam
Published 11/2024
MP4 | Video: h264, 1920×1080 | Audio: AAC, 44.1 KHz
Pass the ISC2 CISSP exam on your 1st attempt, includes a full practice exam!
What you’ll learn
Develop and implement risk management strategies
Classify and secure information assets effectively
Design and maintain secure network architectures
Implement identity and access management protocols
Conduct security assessments and vulnerability testing
Manage and respond to security incidents
Integrate secure practices in software development processes
Apply industry standards and frameworks in information security
Requirements
Minimum of five years of professional experience in two or more CISSP domains (required for CISSP certification)
Basic understanding of networking and information systems
Access to a computer with an internet connection for coursework and the practice exam
Description
Overview
Section 1: Introduction
Lecture 1 Introduction
Lecture 2 Download your free study guide
Lecture 3 Exam Tips
Section 2: Security Management Concepts
Lecture 4 Security Management Concepts
Lecture 5 Code of Ethics (OBJ. 1.1)
Lecture 6 Information Security Concepts (OBJ. 1.2)
Lecture 7 Aligning Security And The Organization (OBJ. 1.3)
Lecture 8 Organizational Roles and Responsibilities (OBJ. 1.3)
Lecture 9 Security Awareness Training And Education (OBJ. 1.12)
Lecture 10 Social Engineering (OBJ. 1.12)
Lecture 11 Personnel Security Policies (OBJ. 1.8)
Lecture 12 Personnel Safety and Security (OBJ. 7.15)
Section 3: Security Governance and Compliance
Lecture 13 Security Governance and Compliance
Lecture 14 Due Care and Due Diligence (OBJ. 1.3)
Lecture 15 Important Laws and Regulations (OBJ. 1.4)
Lecture 16 Licensing and Property Rights (OBJ. 1.4)
Lecture 17 Export and Import Controls (OBJ. 1.4)
Lecture 18 Cybercrime And Data Breaches (OBJ. 1.4)
Lecture 19 Determine Compliance Requirements (OBJ. 1.4)
Section 4: Risk Management
Lecture 21 Risk Management
Lecture 22 Risk Management Concepts (OBJ. 1.9)
Lecture 23 Risk Response And Monitoring (OBJ. 1.9)
Lecture 24 Controls and Countermeasures (OBJ. 1.9)
Lecture 25 Continuous Monitoring (OBJ. 1.9, 7.2)
Lecture 26 Supply Chain Risk Management (OBJ. 1.11)
Section 5: Risk Frameworks
Lecture 27 Risk Frameworks
Lecture 28 Risk Frameworks (OBJ. 1.9)
Lecture 29 NIST Cybersecurity Framework (OBJ. 1.9)
Lecture 30 ISO/IEC 27001 (OBJ. 1.9)
Lecture 31 Understanding PCI DSS (OBJ. 1.9)
Lecture 32 Understanding SABSA (OBJ. 1.9)
Section 6: Risk Assessments
Lecture 33 Risk Assessments
Lecture 34 Understanding Risk Assessments (OBJ. 1.9)
Lecture 35 Conducting Risk Assessments (OBJ. 1.9)
Lecture 36 Control Assessments (OBJ. 1.9)
Lecture 37 Privacy Control Assessments (OBJ. 1.9)
Lecture 38 PCI DSS Assessments (OBJ. 1.9)
Lecture 39 Threat Modeling Concepts (OBJ. 1.10)
Lecture 40 Threat Modeling Methodologies (OBJ. 1.10)
Section 7: Asset Security
Lecture 41 Asset Security
Lecture 42 Classifying Data And Assets (OBJ. 2.1)
Lecture 43 Information and Asset Handling Requirements (OBJ. 2.2)
Lecture 44 Managing System Assets (OBJ. 2.3)
Lecture 45 Data Roles And Responsibilities (OBJ. 2.4)
Lecture 46 Managing The Data Lifecycle (OBJ. 2.4)
Section 8: Data Security Controls
Lecture 49 Data Security Controls
Lecture 50 Understanding Data States (OBJ. 2.6, 7.5)
Lecture 51 Security Control Frameworks (OBJ. 1.3)
Lecture 52 Determining Security Controls (OBJ. 2.6)
Lecture 53 Selecting Security Controls (OBJ. 2.6, 3.3)
Lecture 54 Data Protection Methods (OBJ. 2.6)
Lecture 55 Data Retention Requirements (OBJ. 2.4)
Lecture 56 Managing Data Remanence (OBJ. 2.4)
Section 9: Secure Design Principles
Lecture 57 Secure Design Principles
Lecture 58 Understanding Secure Design (OBJ. 3.5)
Lecture 59 Secure Design Principles (OBJ. 3.1)
Lecture 60 Zero Trust Architecture (OBJ. 3.1, 5.4)
Lecture 61 Privacy By Design (OBJ. 3.1)
Lecture 62 System Security Capabilities (OBJ. 3.4)
Lecture 63 Understanding Security Models (OBJ. 3.2)
Section 10: Secure Architecture Design
Lecture 66 Secure Architecture Design
Lecture 67 System Architectures (OBJ. 3.5)
Lecture 68 Database Systems (OBJ. 3.5)
Lecture 69 Common Criteria (OBJ. 3.5)
Lecture 70 Industrial Control Systems (OBJ. 3.5)
Lecture 71 Secure Access Service Edge (OBJ. 3.1)
Lecture 72 Internet of Things (OBJ. 3.5)
Lecture 73 Microservices (OBJ. 3.5)
Lecture 74 Embedded Systems (OBJ. 3.5)
Lecture 75 High-Performance Computing (OBJ. 3.5)
Lecture 76 Edge Computing Systems (OBJ. 3.5)
Section 11: Virtualization and Cloud Computing
Lecture 77 Virtualization and Cloud Computing
Lecture 78 Virtualized Systems (OBJ. 3.5)
Lecture 79 Containerization (OBJ. 3.5)
Lecture 80 Cloud Deployment Models (OBJ. 3.5)
Lecture 81 Cloud Service Models (OBJ. 3.5)
Lecture 82 Shared Responsibility Model (OBJ. 3.5)
Lecture 83 Virtual Private Cloud (OBJ. 4.1)
Lecture 84 Serverless Computing (OBJ. 3.5)
Section 12: Cryptographic Solutions
Lecture 85 Cryptographic Solutions
Lecture 86 Understanding Cryptography (OBJ. 3.6)
Lecture 87 Cryptographic Methods (OBJ. 3.6)
Lecture 88 Symmetric Ciphers (OBJ. 3.6)
Lecture 89 Asymmetric Ciphers (OBJ. 3.6)
Lecture 90 Quantum Cryptography (OBJ. 3.6)
Lecture 91 Hash Functions (OBJ. 3.6)
Lecture 92 Cryptographic Key Management (OBJ. 3.6)
Lecture 93 Digital Signatures and Certificates (OBJ. 3.6)
Lecture 94 Public Key Infrastructure (OBJ. 3.6)
Section 13: Cryptanalytic Attacks
Lecture 95 Cryptanalytic Attacks
Lecture 96 Vulnerabilities In Cryptographic Systems (OBJ. 3.5)
Section 14: Physical Security
Lecture 100 Physical Security
Lecture 101 Site Design Principles (OBJ. 3.8)
Lecture 102 Facility Design Principles (OBJ. 3.9)
Lecture 103 Facility Security Controls (OBJ. 3.9)
Lecture 104 Facility Infrastructure Security (OBJ. 3.9)
Lecture 105 Fire Prevention, Detection, and Suppression (OBJ. 3.9)
Lecture 106 Physical Security Controls (OBJ. 7.14)
Section 15: Network Components
Lecture 107 Network Components
Lecture 108 Hardware Operations (OBJ. 4.2)
Lecture 109 Network Infrastructure Operations (OBJ. 4.2)
Lecture 112 Network Monitoring (OBJ. 4.1)
Section 16: Networking Concepts
Lecture 113 Networking Concepts
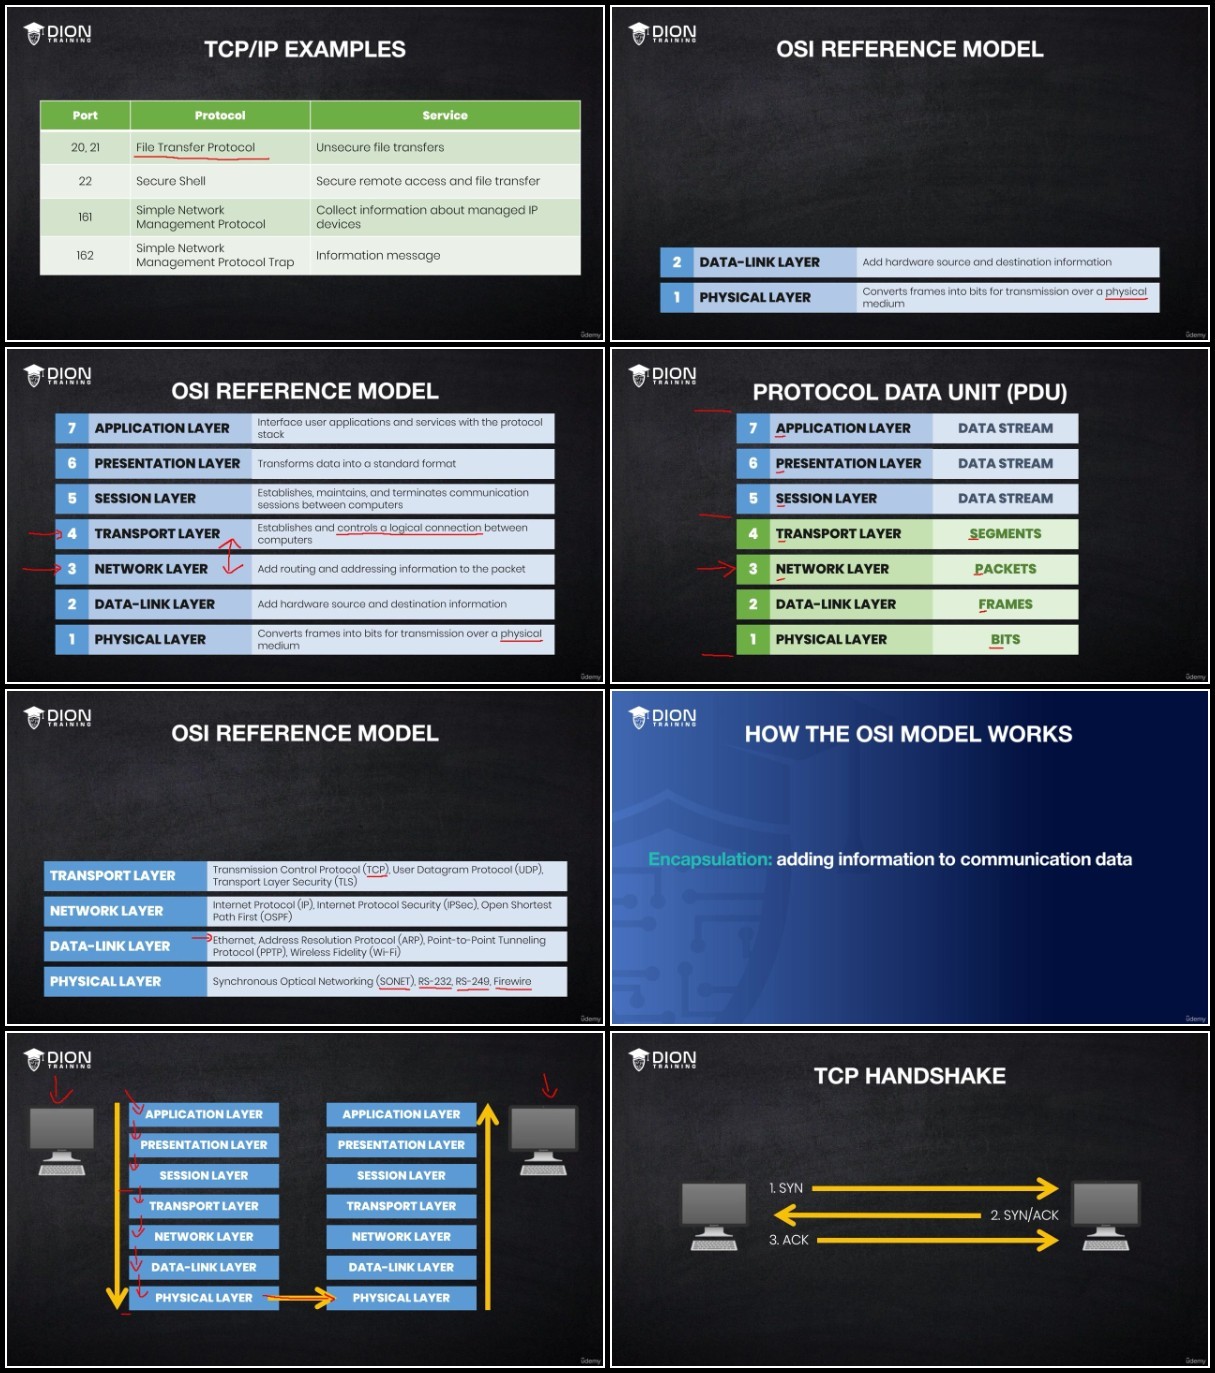
Lecture 114 TCP/IP and OSI Models (OBJ. 4.1)
Lecture 115 IP Networking (OBJ. 4.1)
Lecture 116 LAN Communications (OBJ. 4.1)
Lecture 117 Communication Protocols (OBJ. 4.1)
Lecture 118 Multilayer Protocols (OBJ. 4.1)
Lecture 119 Converged Protocols (OBJ. 4.1)
Lecture 120 Data Communications (OBJ. 4.3)
Lecture 121 Virtualized Networks (OBJ. 4.3)
Section 17: Network Architectures
Lecture 122 Network Architectures
Lecture 123 Content Distribution Networks (OBJ. 4.1)
Lecture 124 Software Defined Networks (OBJ. 4.1)
Lecture 125 Application Programming Interfaces (OBJ. 4.1)
Lecture 126 Network Functions Virtualization (OBJ. 4.1)
Section 18: Secure Network Design
Lecture 127 Secure Network Design
Lecture 128 Transport Architecture (OBJ. 4.1)
Lecture 129 Performance Metrics (OBJ. 4.1)
Lecture 130 Network Traffic Flows (OBJ. 4.1)
Lecture 131 Physical Network Segmentation (OBJ. 4.1)
Lecture 132 Logical Network Segmentation (OBJ. 4.1)
Lecture 133 Micro-Segmentation (OBJ. 4.1)
Lecture 134 Edge Networks (OBJ. 4.1)
Section 19: Network Security and Attacks
Lecture 135 Network Security and Attacks
Lecture 136 Firewalls Concepts (OBJ. 7.7)
Lecture 137 Types of Firewalls (OBJ. 7.7)
Lecture 138 Firewall Architecture (OBJ. 7.7)
Lecture 139 IP Security (OBJ. 4.1)
Lecture 140 Endpoint Security (OBJ. 4.2)
Lecture 141 Network Access Control (OBJ. 4.2)
Lecture 142 Reconnaissance Attacks (OBJ. 4.2)
Lecture 143 Spoofing and Poisoning Attacks (OBJ. 4.2)
Lecture 144 Denial of Service Attacks (OBJ. 4.2)
Section 20: Secure Communications
Lecture 145 Secure Communications
Lecture 146 Remote Access Security (OBJ. 4.3)
Lecture 147 Multimedia Collaboration (OBJ. 4.3)
Lecture 148 Voice Communications (OBJ. 4.3)
Lecture 149 Email Security (OBJ. 4.3)
Lecture 150 Backhaul Networks (OBJ. 4.3)
Section 21: Wireless Networking
Lecture 151 Wireless Networking
Lecture 152 Wireless Networks (OBJ. 4.1)
Lecture 153 Wireless Network Modes (OBJ. 4.1)
Lecture 154 Wireless Network Security (OBJ. 4.1)
Lecture 155 Mobile Device Management (OBJ. 3.5, 4.1)
Section 22: Identity Management
Lecture 156 Identity Management
Lecture 157 Establishing Identity (OBJ. 5.2)
Lecture 158 Identity Management (OBJ. 5.2)
Lecture 159 Federated Identity Management (OBJ. 5.6)
Lecture 160 Delegated Identity Management (OBJ. 5.3)
Lecture 161 Identity and Access Lifecycle (OBJ. 5.5)
Section 23: Authentication Mechanisms
Lecture 162 Authentication Mechanisms
Lecture 163 Authentication Systems (OBJ. 5.6)
Lecture 164 Authentication Factors (OBJ. 5.2)
Lecture 165 Biometric Authentication (OBJ. 5.2)
Lecture 166 Single Sign On (OBJ. 5.2)
Lecture 167 OAuth and OIDC (OBJ. 5.6)
Lecture 168 Kerberos (OBJ. 5.6)
Lecture 169 Credential Management Systems (OBJ. 5.2)
Lecture 170 Just-In-Time Access (OBJ. 5.2)
Section 24: Access and Authorization
Lecture 173 Access and Authorization
Lecture 174 Accountability (OBJ. 5.4)
Lecture 175 Access Authorization (OBJ. 5.4)
Lecture 176 Controlling Logical Access (OBJ. 5.1)
Lecture 177 Session Management (OBJ. 5.2)
Lecture 178 Password Attacks (OBJ. 5.2)
Section 25: Security Test and Assessment
Lecture 179 Security Test and Assessment
Lecture 180 Security Test And Assessment Planning (OBJ. 6.1, 6.5)
Lecture 181 Performance and Risk Indicators (OBJ. 6.3)
Lecture 182 Collecting Security Data (OBJ. 6.3)
Lecture 183 Account Management Data (OBJ. 6.3)
Lecture 184 Verifying Training and Awareness (OBJ. 6.3)
Lecture 185 Disaster Recovery and Business Continuity Data (OBJ. 6.3)
Section 26: Conduct Security Testing
Lecture 186 Conduct Security Testing
Lecture 187 Vulnerability Assessments (OBJ. 6.2)
Lecture 188 Vulnerability Scanning (OBJ. 6.2)
Lecture 189 Penetration Testing (OBJ. 6.2)
Lecture 190 Penetration Testing Phases (OBJ. 6.2)
Lecture 191 Log Reviews (OBJ. 6.2)
Lecture 192 Software Testing Methods (OBJ. 6.2)
Lecture 193 Software Code Reviews (OBJ. 6.2)
Lecture 194 Misuse Testing (OBJ. 6.2)
Lecture 195 Interface Testing (OBJ. 6.2)
Lecture 196 Compliance Testing (OBJ. 6.2)
Lecture 197 Test Coverage Analysis (OBJ. 6.2)
Lecture 198 Analyzing Test Results (OBJ. 6.4)
Section 27: Detective And Preventative Measures
Lecture 199 Detective And Preventative Measures
Lecture 200 Security Operation Concepts (OBJ. 7.4)
Lecture 201 Detective And Preventative Concepts (OBJ. 7.7)
Lecture 202 IDS/IPS Systems (OBJ. 7.2)
Lecture 203 Honeypots and Honeynets (OBJ. 7.7)
Lecture 204 Malicious Software (OBJ. 7.7)
Lecture 205 Anti-Malware (OBJ. 7.7)
Section 28: Logging and Monitoring
Lecture 207 Logging and Monitoring
Lecture 208 Logging and Monitoring (OBJ. 7.2)
Lecture 209 Security Information and Event Management (OBJ. 7.2)
Lecture 210 Threat Intelligence (OBJ. 7.2)
Lecture 211 MITRE ATT&CK Framework (OBJ. 7.2)
Lecture 212 Cyber Kill Chain (OBJ. 7.2)
Lecture 213 Security Orchestration, Automation and Response (OBJ. 7.2)
Lecture 214 Behavior Analytics (OBJ. 7.2)
Section 29: Configuration Management
Lecture 215 Configuration Management Introduction
Lecture 216 Configuration Management (OBJ. 7.3)
Lecture 217 System Patch Management (OBJ. 7.8)
Lecture 218 Change Control (OBJ. 7.9)
Lecture 219 Software Configuration Management (OBJ. 8.1, 8.2)
Lecture 220 Media Management (OBJ. 7.5)
Section 30: Incident Management
Lecture 221 Incident Management Introduction
Lecture 222 Incident Management (OBJ. 7.6)
Lecture 223 Security Investigations (OBJ. 7.1)
Lecture 224 Cyber Related Investigations (OBJ. 1.5)
Lecture 225 Evidence Collection and Handling (OBJ. 7.1)
Lecture 226 Digital Forensics (OBJ. 7.1)
Lecture 227 Digital Forensic Incident Response (OBJ. 7.1)
Section 31: Business Continuity and Disaster Recovery
Lecture 228 Business Continuity and Disaster Recovery
Lecture 229 Business Continuity Planning (OBJ. 1.7, 7.13)
Lecture 230 Business Impact Analysis (OBJ. 1.7)
Lecture 231 Disaster Recovery Planning (OBJ. 7.10)
Lecture 232 Disaster Recovery Strategies (OBJ. 7.10)
Lecture 233 Disaster Recovery Sites (OBJ. 7.10)
Lecture 234 Data Backup Strategies (OBJ. 7.10)
Lecture 235 Disaster Recovery Processes (OBJ. 7.11)
Lecture 236 Disaster Recovery Testing (OBJ. 7.12)
Section 32: Software Development Security
Lecture 237 Software Development Security
Lecture 238 Software Development Lifecycle (OBJ. 8.1)
Lecture 241 Agile Development (OBJ. 8.1)
Lecture 242 DevOps and DevSecOps (OBJ. 8.1, 8.2)
Lecture 243 Software Maturity Models (OBJ. 8.1)
Lecture 244 Software Operations And Maintenance (OBJ. 8.1)
Lecture 245 Integrated Product Teams (OBJ. 8.1)
Lecture 246 Code Repositories (OBJ. 8.2)
Section 33: Application Security
Lecture 247 Application Security
Lecture 248 Programming Languages (OBJ. 8.2)
Lecture 249 Application Security Testing (OBJ. 8.2)
Lecture 250 Software Assurance (OBJ. 8.3)
Lecture 251 Acquired Software Security (OBJ. 8.4)
Lecture 252 Application Attacks (OBJ. 8.5)
Lecture 256 Software API Security (OBJ. 8.5)
Lecture 257 Secure Coding Practices (OBJ. 8.5)
Lecture 258 Software-Defined Security (OBJ. 8.5)
Section 34: Practice Exam
Section 35: Conclusion
Lecture 259 Conclusion
Lecture 260 BONUS: What comes next?
Security Managers and Consultants,IT and Network Security Professionals,Systems Engineers and Administrators,Information Security Analysts,Compliance Officers,Risk Management Professionals,Software Developers interested in secure development practices
TurboBit
https://www.keeplinks.org/p27/67d3b86c66ca1
RapidGator
https://www.keeplinks.org/p27/67d3c29684038
FileFactory